



A critical security flaw, identified as CVE-2023-27997, has left hundreds of thousands of FortiGate firewalls vulnerable to attacks. Despite a recent update released by Fortinet to address the issue, offensive security solutions company Bishop Fox reports that over 300,000 devices remain exposed on the public internet.
The Vulnerability and its Severity
The vulnerability, classified as a remote code execution flaw, scores a severity rating of 9.8 out of 10. It stems from a heap-based buffer overflow problem within FortiOS, the operating system that integrates Fortinet networking components into the vendor’s Security Fabric platform. The flaw allows unauthenticated attackers to remotely execute code on susceptible devices with an exposed SSL VPN interface.
Fortinet’s Response and Patch Availability
Fortinet promptly addressed the vulnerability on June 11, releasing firmware updates for FortiOS versions 6.0.17, 6.2.15, 6.4.13, 7.0.12, and 7.2.5. However, despite the urgent call to patch affected devices, Bishop Fox’s recent findings suggest that a significant number of FortiGate firewalls are still vulnerable to attacks and accessible over the public internet.
Also Read: Snappy: A tool that detects rogue Wi-Fi access points on open networks
Identification and Estimation of Vulnerable Devices
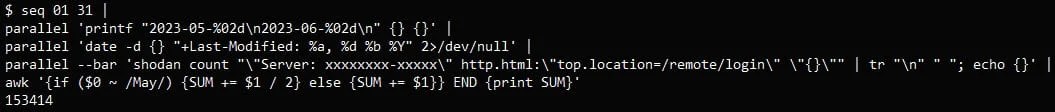
By utilizing the Shodan search engine, Bishop Fox researchers identified devices with exposed SSL VPN interfaces. They specifically targeted appliances that responded with an HTTP header leading to the “/remote/login” endpoint.

Out of the 489,337 devices discovered, further investigation revealed that 153,414 had been updated to a secure FortiOS version. This indicates that approximately 335,900 FortiGate firewalls remain vulnerable, surpassing previous estimations of 250,000 devices.
Outdated Firmware Amplifies the Risk
Bishop Fox researchers made an alarming discovery regarding the exposed FortiGate devices. A significant number of them have not received updates in the past eight years, with some still operating on FortiOS 6, which reached end of support on September 29 last year. Consequently, these devices are susceptible to multiple critical-severity vulnerabilities for which proof-of-concept exploit code is publicly available.
Demonstration of the Vulnerability
To demonstrate the severity of CVE-2023-27997, Bishop Fox created an exploit that showcases the ability to execute code remotely on vulnerable devices. The exploit efficiently “smashes the heap, connects back to an attacker-controlled server, downloads a BusyBox binary, and opens an interactive shell.” According to Bishop Fox, this exploit demonstrates the vulnerability more effectively and executes faster than previous demonstrations by Lexfo.

Conclusion: Urgent Action Required
The widespread vulnerability in FortiGate firewalls necessitates immediate action from organizations utilizing these devices. Patching affected devices with the latest FortiOS firmware is crucial to mitigate the risk of remote code execution. Neglecting these security measures could expose networks and sensitive data to potential attacks. Stay informed, follow the recommended guidelines, and protect your infrastructure from potential threats.


Leave a Reply