



Key Highlights
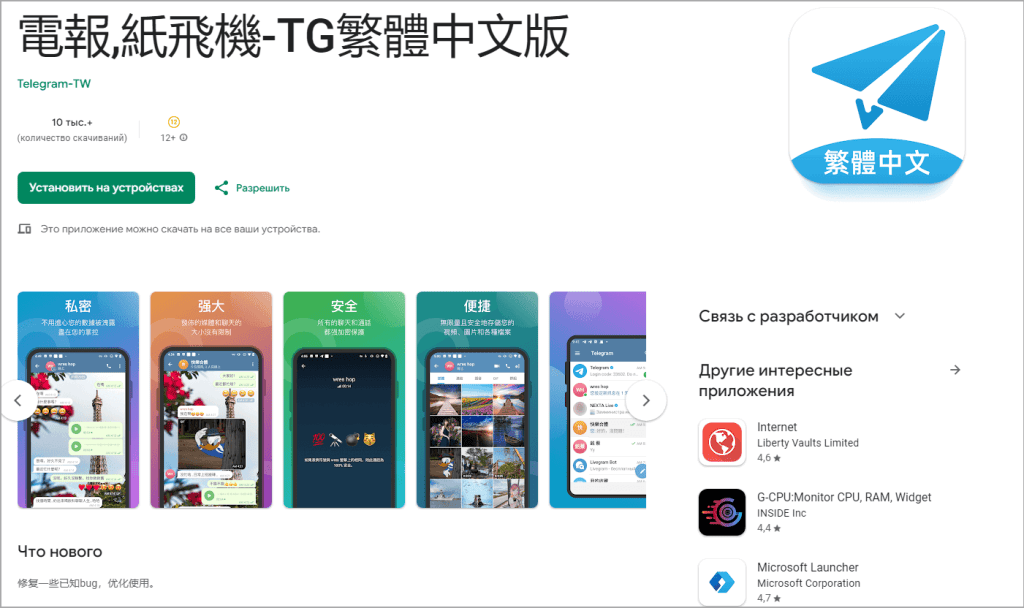
- Malicious Telegram clones for Android containing spyware were downloaded over 60,000 times on Google Play.
- The apps targeted Chinese-speaking users and the oppressed Uighur minority, suggesting state surveillance motives.
- The spyware was designed to steal messages, contacts, usernames, phone numbers and other sensitive user data.
A new wave of Android malware has infiltrated over 60,000 devices by posing as malicious clones of the popular Telegram messaging app. Security researchers at Kaspersky discovered the spyware campaign targeting Chinese-speaking users, including the oppressed Uighur minority.
The tainted apps contained additional spyware code designed to steal messages, contacts, usernames, phone numbers and other sensitive data. Kaspersky reported the offending apps to Google, but some still remained available for download at the time of publication.
Going Undercover as Faster Telegram Alternatives
These rogue Telegram clones circumvented Google Play protections by promoting themselves as superior versions of Telegram. Descriptions claimed increased speed and efficiency compared to the official app. This false allure successfully tricked thousands into downloading the malware in disguise.

Once installed, the apps added an extra software package capable of exfiltrating personal information and copying messages to a remote server run by the attackers. The stolen data underwent encryption before covert transmission to the spying operators.
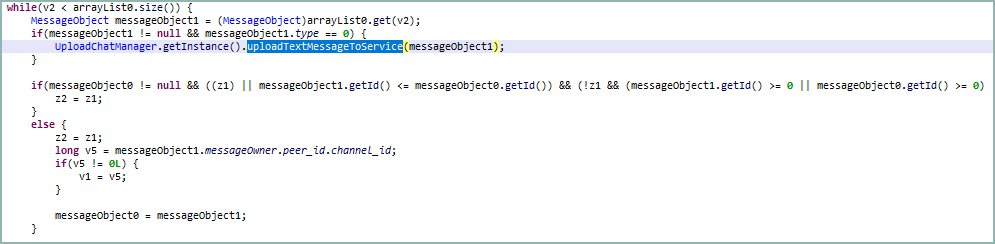
In addition to copying messages, the implanted spyware constantly monitored for updates to username, user ID and contact lists within the infected Telegram clone. This granted the data thieves continuous access even as details changed within accounts.
Signs of State-Sponsored Monitoring
While the creators remain unconfirmed, Kaspersky noted the apps’ Chinese language targeting and focus on Uighur users point to state surveillance. China’s repression of the Uighur minority is well documented, including digital spying and tracking mechanisms.
Also Read: Toyota production grinds to a halt: How a lack of server storage crippled the automotive giant
These trojanized apps represent only the latest in a string of malware campaigns aimed at compromise Chinese-speaking users through tainted messaging apps. Earlier this year, over two dozen fake Telegram and WhatsApp sites were found spreading spyware-injected versions of both apps.
With messaging platforms holding tremendous sensitive value, users should stick to reputable app sources like Google Play and scrutinize any messaging clones claiming enhanced features or privacy. Verifying authenticity can help avoid installing spyware in disguise.
For Google, the recurring incidents signal an urgent need for enhanced protections and verification mechanisms within the Play Store. While these apps were removed post-discovery, thousands still fell victim during their availability. Tougher screening and validation of publishers may help curb similar spyware masquerading as trusted apps.


Leave a Reply